Password and Account Hygiene for Adult AI Chat
Account hygiene on an adult platform is mostly ordinary password practice applied consistently, and the arithmetic is unforgiving: one reused credential is enough to link accounts you intended to keep apart. On a Porn Chat AI style service there are also two extra levers most people never use — the report route inside every content page and the published compliance statement.
Key takeaways
- One unique credential per service, stored in a manager, removes the single largest cause of account crossover.
- The email address behind the account matters more than the password, because it is the recovery path.
- Sign out on shared hardware and set a device passcode: a signed-in session needs no password at all.
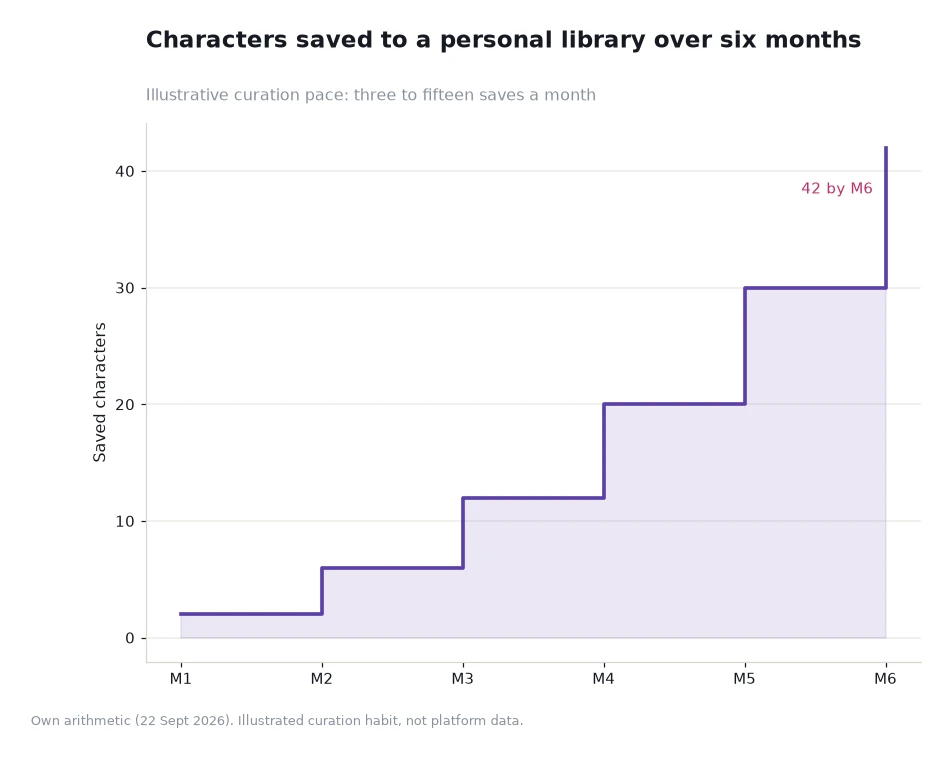
- A library that reaches 42 saved characters in six months is a real archive — worth reviewing at least quarterly.
Start with the credential, not the platform
Reuse is the failure mode that matters. A password used on a forum and on an adult chat account turns an unrelated leak into a direct link between your identity and your interests. A password manager solves this by generating a different string for every service, so no single breach produces a credential that works anywhere else. The generated strings do not need to be memorable; that is the point of storing them.
Passphrase length beats symbol theatre. Three or four unrelated words are easier to type on a phone keyboard than a twelve-character jumble and are no weaker for that reason. Where the service offers a second factor, enable it, and apply the same rule to the email account that receives the codes, because a second factor routed through a compromised inbox protects nothing.
The email address is the real account
Almost every recovery flow runs through the address on file. If that inbox is accessible to someone else, or is the same address you publish everywhere, the account's security is capped at the inbox's security. A separate address used only for adult services is a small organisational step with a large structural effect: it keeps recovery mail out of a shared family inbox and stops password resets from appearing in front of other people.
Crushon describes its environment as private and secure, with state-of-the-art encryption, and that wording is worth quoting accurately rather than upgrading. Encryption protects data in transit and at rest; it does not stop a household member from opening an unlocked phone. The practical work of keeping an account separate is done at the level of devices and mailboxes, which is where the reader has both control and responsibility.
Devices, sessions and the quiet risks
An unlocked phone with a signed-in session is a bigger exposure than a weak password, because it requires no knowledge at all, only access. Two settings cover most of that gap: a device passcode that is not shared, and a habit of signing out on any computer that is not yours. Browser autofill is convenient and also the reason a saved credential can be used by the next person on the machine, so it belongs only on hardware you control.
Keep the platform's own routes in view as well. Every content page carries a report option according to the content removal policy, and the public support address is the same channel for compliance questions and the 2257 statement. Using those routes rather than a third-party forum is the fastest way to have something reviewed, and it keeps the interaction inside the platform's own processes.
| Step | Failure it prevents | Cadence |
|---|---|---|
| Unique password per service | Credential reuse linking unrelated accounts | Set once, replaced when a provider reports a breach |
| Password manager | Memorable-but-repeated strings | Daily use, backup export twice a year |
| Separate recovery email | Reset links landing in a shared inbox | Set once, checked monthly |
| Device passcode and sign-out | Anyone with the hardware reading a live session | Every session on shared hardware |
| Library review | Saved lists growing past what you can supervise | Quarterly: 12 saves after three months, 42 after six |
Worked example: how fast a library needs supervising
Illustrative assumption: a reader saves characters at a modest starting pace that accelerates as the catalogue becomes familiar. Month one ends with 2 saves. Adding 4 takes it to 6, adding 6 takes it to 12, adding 8 takes it to 20, adding 10 takes it to 30, and adding 12 takes it to 42 at the end of month six. The monthly additions run from 4 to 12, inside a three-to-fifteen-a-month band.
Read the same numbers by quarter. Months one to three deliver 12 saves. Months four to six add 12, 20 and 30 minus the 12 already held, which is 30 new saves — two and a half times the first quarter's total. A library that doubles and then some inside a single quarter is not something you can keep in your head, which is why a scheduled review beats an improvised one. Six months of that pace is 42 saved characters, and 42 items is a list that deserves a proper pass rather than a glance.
Keeping an ai porn chat account tidy
Tidiness is a review habit rather than a setting. Once a quarter, list the characters you actually revisit, remove the ones you do not, and check whether the email address on the account is still one you control and still separate from your everyday inbox. Fifteen minutes four times a year is an hour of maintenance annually, which is a small cost for knowing exactly what is stored where.
While you are there, confirm the recovery details still work: a reset link that cannot reach you is worth less than nothing, because it is a false sense of safety. Readers who want the platform's side of these questions in its own words can read the content removal policy and the 2257 compliance statement, both of which describe what the site holds and how it responds to reports.
Frequently asked questions
Is a password manager safe for adult accounts?
It is safer than reuse, which is the alternative most people practise. A manager holds a different generated credential for every service, so one leaked password does not open another account, and the master credential is the only one you have to protect carefully.
Do I need a separate email address?
It is strongly advisable rather than mandatory. Recovery mail is the one message stream that reveals which services you use, so routing it to an address of its own keeps resets and login alerts away from a shared inbox.
How often should a saved library be reviewed?
Quarterly at minimum. At the illustrated pace a library reaches 12 saves in three months and 42 in six, which is more than most people can supervise from memory.
Do the boring things once
Set a unique credential, store it in a manager, route recovery through a private address, put a passcode on the phone, and sign out on anything you do not own. None of those steps takes more than a few minutes, and together they remove the failure modes that cause the most damage. Then put the quarterly review in a calendar and forget about it until it arrives.
Data and sources: the Crushon content removal policy, which describes the report option on every content page and the public support address, and the 2257 statement last updated 8 February 2025[1], read 22 Sept 2026. The six-month library progression is an illustrative figure, not platform data. Only readers who are 18 or above should act on this guidance.